Introduction: What AI Risk Management Software Actually Does
AI risk management software is a category of tools designed to help organizations identify, assess, and mitigate risks specific to artificial intelligence systems, including model behavior, data flows, bias, and unauthorized usage. For businesses with 25 to 100 employees, these platforms answer a question that spreadsheets and annual audits cannot: what AI is running in our environment right now, and is it behaving the way we expect?
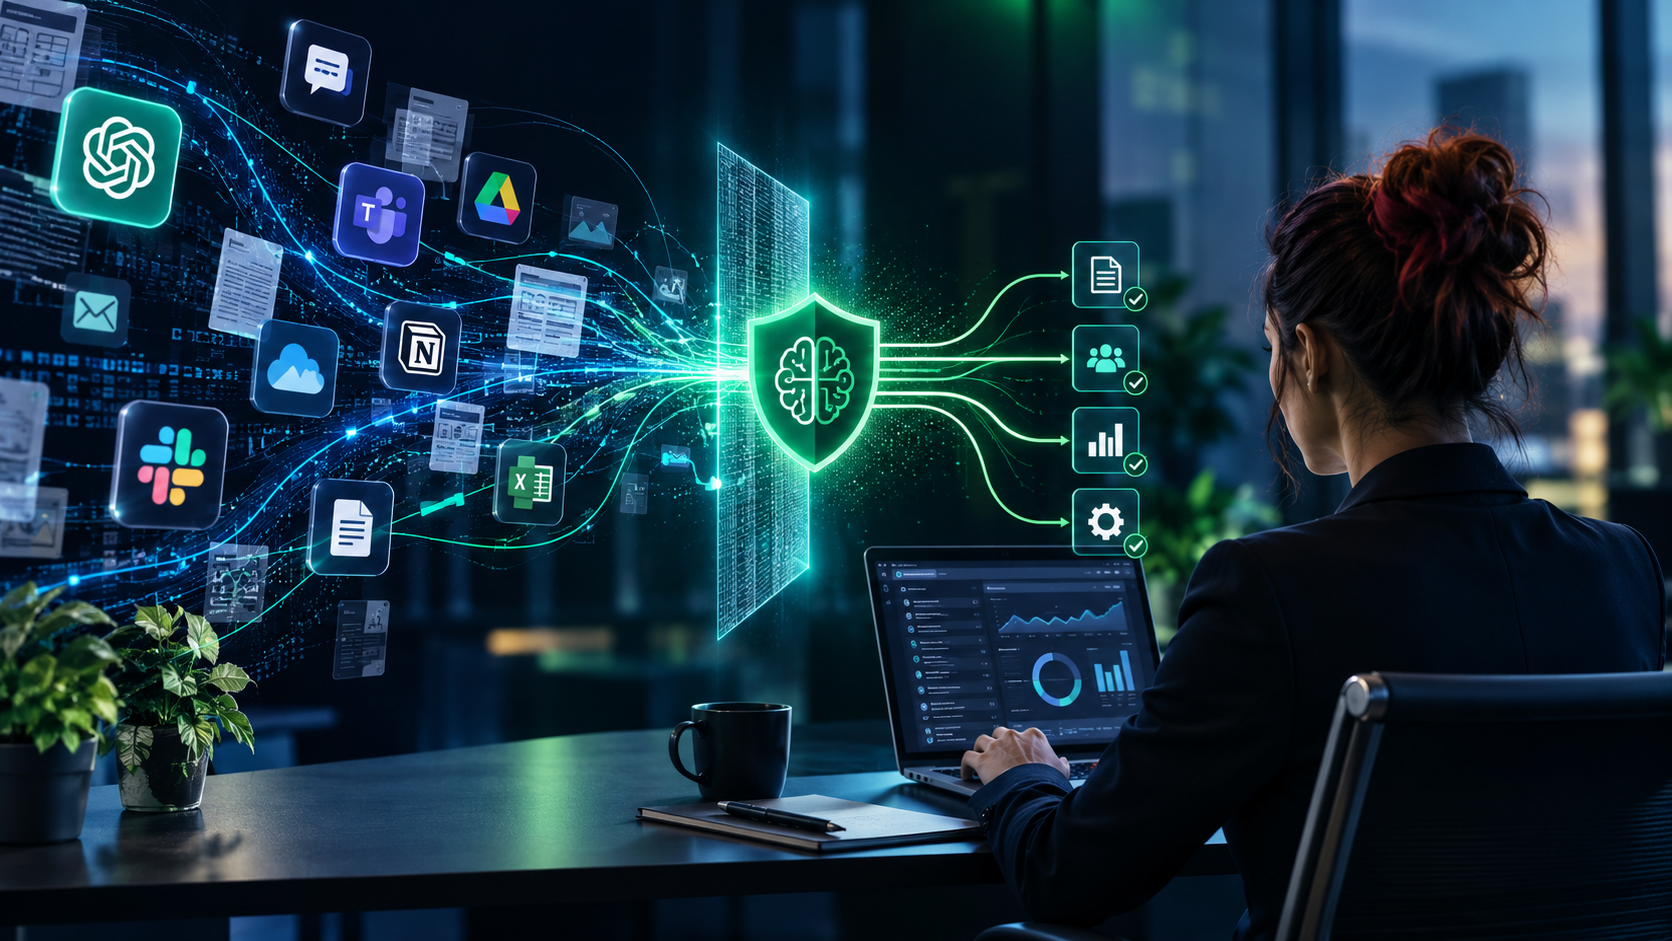
Unlike generic cybersecurity or GRC tools, AI risk management software combines automation, analytics, and policy workflows to address risks that are unique to AI and machine learning: data leakage through chatbots, model drift in analytics tools, shadow AI adopted by employees without IT’s knowledge, and regulatory gaps that traditional security products were never built to catch. AI risk management software shifts organizations from reactive to proactive strategies for handling these issues.
For Richmond, VA businesses, where law firms handle privileged documents, healthcare providers manage PHI, and financial services firms process sensitive client data, these risks are not abstract. They translate directly to client trust, regulatory compliance, and operational continuity.
At Technology Assurance Group (TAG), we help small and mid-sized businesses select, configure, and operate AI risk management software as part of a broader managed IT and cybersecurity program. These tools are not reserved for Fortune 500 companies. Modern cloud platforms can be right-sized for organizations with flat-rate IT budgets and small teams.
This article walks through the benefits, core features, relevant frameworks like the NIST AI RMF, selection criteria, and how TAG helps implement a practical risk management framework for AI.
Key Takeaways for Busy Executives
-
AI risk management software focuses on risks that generic IT security tools miss: model bias, data leakage through AI prompts, unauthorized AI tool usage, and regulatory gaps tied to AI systems.
-
You do not need an in-house data science team. TAG implements and manages these tools as part of a broader risk management framework, under a flat-rate model.
-
95% of U.S. companies utilize AI in production as of 2023, and 78% of organizations treat AI as an emerging risk in 2024. If your business uses AI, the question is not whether to govern it, but how.
-
Aligning with the NIST AI Risk Management Framework and ISO 42001 is achievable for SMBs when the right software and expert guidance work together.
-
Practical outcomes include fewer security incidents related to AI, smoother compliance audits, better visibility into shadow AI, and stronger data integrity across AI-powered workflows.
-
Software alone is not enough. Effective AI risk management requires clear ownership, proportional controls, and regular review cycles.
What Is AI Risk Management Software?
AI risk management software is a class of platforms built to monitor, assess, and govern the behavior of AI and machine learning systems across their lifecycle. Where traditional GRC or cybersecurity tools focus on network intrusion, malware, or access control, AI risk management software examines what models are in use, what data flows into them, how they perform over time, and whether they comply with organizational policies and regulations.
These platforms ingest logs, model metadata, prompt histories, and business data to detect anomalies, policy violations, and emerging AI risks. The AI risk management market includes AI-specific governance platforms and enterprise GRC platforms with AI add-on modules; AI platforms diverge in focus between compliance, governance, and operational workflow automation.
Core functions at a high level:
- Cataloging AI systems: building an inventory of every AI tool, chatbot, analytics model, or vendor-provided AI feature in use.
- Evaluating risk levels: automated or semi-automated scoring based on data sensitivity, regulatory exposure, and model behavior.
- Enforcing policies: defining and applying rules for acceptable use, data access, and model updates.
- Tracking mitigation tasks: assigning remediation work when issues are found.
- Generating audit-ready reports: evidence collection mapped to compliance frameworks.
For SMBs, this looks practical. A law firm using an AI document summarizer can monitor whether confidential client files are being uploaded to an unvetted model. A medical office running AI-assisted billing can detect when model versions change without review or when PHI enters a pipeline beyond what is necessary. AI risks include model bias, data leakage, and adversarial attacks; these tools are designed to surface those issues before they become breaches or compliance failures.
Some platforms are standalone. Others extend existing risk management software, SIEM, or compliance tools already deployed in an organization’s environment.

How AI Risk Management Software Fits into a Risk Management Framework
Software is an enabler, not a replacement, for a structured risk management framework. An organization still needs defined policies, ownership, and review processes. The tool operationalizes those decisions by mapping risks, controls, and evidence into day-to-day workflows.
The NIST AI Risk Management Framework provides structured risk management guidance organized around core functions: Govern, Map, Measure, and Manage. ISO 31000 provides principles for managing risks across all sectors and serves as a foundational reference for broader risk programs. AI risk management frameworks address ethical, legal, and technical vulnerabilities; the software layer makes those frameworks actionable instead of aspirational.
A typical risk management framework follows steps that software supports at each stage:
- Risk identification: the platform scans for AI assets, data flows, and potential risks across the environment.
- Risk assessment: automated scoring and classification assign risk ratings based on data sensitivity, regulatory context, and technical exposure.
- Risk treatment: workflows route remediation tasks to appropriate team members with deadlines and evidence requirements.
- Continuous monitoring: always-on observation of AI systems performance, data access, and policy compliance.
- Review: scheduled reporting and audit trails allow leadership to verify that controls remain effective.
TAG helps SMBs translate high-level frameworks into practical control sets inside their chosen tools, rather than attempting to implement the NIST AI RMF or ISO 42001 purely on paper. The question executives should ask: can we prove, not just claim, that AI risks are being addressed and reviewed on a schedule?
The Dual Focus: Managing AI Risk and Using AI for Risk Management
Two intertwined topics sit at the center of this category. First, artificial intelligence is a new risk source: models can behave unpredictably, leak data, or perpetuate bias. Second, AI is a powerful capability inside risk management software itself, used to detect threats faster than human-only analysis.
Many modern platforms embed machine learning algorithms and predictive analytics to spot anomalies in network traffic, user behavior, or transaction data. AI can analyze large datasets to predict potential risks, and AI enhances decision-making by providing data-driven recommendations that risk managers would otherwise spend hours assembling manually. Automating routine tasks allows risk analysts to focus on strategic decision making rather than data gathering.
On the other side, AI-specific governance features track model versions, monitor for drift, log prompts to generative AI tools, and enforce acceptable use policies. A small financial services firm could use an AI-enabled dashboard to prioritize vulnerability remediation based on business impact while simultaneously monitoring whether its own AI-powered customer analytics tool is accessing data it should not.
TAG evaluates both sides when advising clients. How much AI should your security tooling use? And how do you keep that usage itself governed and auditable? The two questions are inseparable in any responsible AI development and deployment strategy.
Core Capabilities of Modern AI Risk Management Software
Modern platforms combine analytics, workflow, and documentation capabilities aligned to frameworks like the NIST AI RMF and ISO 42001. AI-driven software enhances operational efficiency in risk management processes by replacing manual tracking with automated detection, scoring, and reporting.
Not every SMB needs every advanced feature. TAG helps prioritize capabilities based on industry, organization size, and risk tolerance. Below are the capabilities that matter most, with examples relevant to regulated sectors common in Virginia.
- AI inventory and model registry: automatic detection and cataloging of every AI tool in use, including vendor-embedded features. A healthcare practice discovers its EHR vendor added AI-powered note summarization without notifying administrators.
- Risk identification workflows: structured processes for flagging and classifying new AI related risks as they emerge. A legal firm identifies that a browser extension used by paralegals sends document text to a third-party AI service.
- Continuous monitoring: always-on observation of AI models, API calls, and data access patterns. A financial advisory firm receives an alert when an employee’s AI usage spikes outside business hours.
- Vulnerability management integration: ingesting scan results from security tools to create a unified risk view. AI-specific weaknesses like prompt injection or exposed model APIs appear alongside traditional IT vulnerabilities.
- Regulatory compliance mapping: built-in control libraries mapped to HIPAA, GDPR, Virginia privacy laws, and AI-specific standards. Templates reduce the burden on SMBs without dedicated compliance teams.
- Audit-ready reporting: exportable evidence packages with version history, prompt logs, data lineage, and risk scores.
According to a 2026 comparison of 12 AI risk management tools, platforms like Microsoft Purview, ServiceNow AI Governance, and IBM watsonx.governance provide varying levels of unified coverage across models, workflows, agents, and drift monitoring.
AI-Powered Risk Identification and Assessment
AI risk management software uses machine learning and pattern recognition to strengthen risk identification beyond what manual spreadsheets and periodic check-ins can deliver. AI minimizes human error and cognitive biases in risk assessments by applying consistent criteria across every asset, every time.
These tools analyze logs, transactions, and user activity to flag suspicious patterns: unusual data exports to unfamiliar AI APIs, abnormal login behavior on AI platforms, or prompts sent to LLMs that contain sensitive keywords. AI can forecast potential risks before they materialize, allowing risk teams to act on leading indicators rather than waiting for an incident report.
Automated scoring and classification help executives see which risks need immediate attention versus longer-term remediation. AI systems can conduct faster and more accurate risk assessments than manual processes, particularly when evaluating dozens or hundreds of AI-related assets across a growing SaaS environment.
A practical example: an SMB discovers over-permissive access to an AI-based HR analytics tool because the platform flagged high-risk data usage patterns; the tool had access to salary and performance data for the entire company, assigned during initial setup and never reviewed. TAG tunes these risk rules so SMBs avoid false positives that overwhelm small teams while still catching issues that matter.
Continuous Monitoring and Early-Warning Alerts
Continuous monitoring in this context means always-on observation of AI systems, data flows, and control performance, replacing quarterly checklists with real-time awareness. AI risk management tools provide real-time monitoring and alerting for anomalies, and AI governance frameworks emphasize continuous monitoring of risks throughout the AI lifecycle.
Modern tools watch for specific indicators:
- Model drift, where an AI system’s outputs gradually shift from expected behavior
- Unexpected spikes in API calls to external AI services
- New third-party integrations that were not approved
- Unusual access to sensitive datasets by AI-powered applications
- AI systems continuously monitor data streams for emerging threats that manual review would miss
Alerting rules and thresholds can be aligned with the organization’s risk appetite. A 30-person law firm does not need the same alert volume as a 10,000-person enterprise. The goal is to avoid alarm fatigue while surfacing real threats quickly. AI risk management frameworks must include continuous monitoring and improvement to remain effective.
These tools integrate with existing monitoring stacks, including SIEM, endpoint detection, and cloud security tools, that TAG commonly manages for clients. Continuous monitoring is essential to maintaining data integrity and timely vulnerability management for AI-related assets.

Data Integrity, Privacy, and Governance Controls
Bad or exposed data leads directly to bad decisions and compliance failures. Data integrity and privacy sit at the center of trustworthy AI, and AI risk management software helps reduce data leaks and misuse by tracking exactly what data enters each AI system and who has access.
These platforms track data lineage for AI systems: where training data and operational data originate, who can access them, and how they are protected. AI compliance includes monitoring data quality and reliability to ensure that AI outputs remain accurate and that the underlying data has not been corrupted or poisoned. Data poisoning, where training data is deliberately manipulated to distort model behavior, is a risk that governance controls can help detect early.
Privacy-preserving features include:
- Masking sensitive fields before data enters AI processing pipelines
- Enforcing data minimization so AI tools only access what they need
- Logging which AI tools touch regulated data such as PHI, PCI, or PII
- Tracking whether AI models maintain data integrity across updates and retraining
Many platforms map controls directly to regulations like GDPR, HIPAA, and state privacy laws, providing built-in templates instead of forcing SMBs to design governance from scratch. AI can perpetuate existing societal biases, leading to unfair outcomes; governance controls that monitor for bias in both structured and unstructured data are part of ethical AI practices that these tools support.
TAG configures these controls so they are realistic for a 25 to 100 person organization, avoiding large-enterprise patterns that create unnecessary overhead.
Vulnerability Management for AI Systems
AI systems introduce new classes of vulnerabilities that traditional IT security scanning was not designed to find. Exposed model APIs, prompt injection attacks, insecure training data pipelines, and insufficient access controls on AI endpoints all need to be folded into the existing vulnerability management program. AI risks include security vulnerabilities and operational failures that can cascade through connected systems.
Some risk management platforms ingest scan results from tools like Qualys, AccuKnox (which automates checks for 30+ compliance standards), or other scanners to create a unified view of both traditional IT weaknesses and AI-specific issues. AI systems can fail due to bugs or data inconsistencies; combining technical severity with business context helps prioritize remediation. A model that supports patient billing carries different risk weight than one used for internal analytics.
TAG routinely uses vulnerability data to create practical remediation roadmaps, scheduling work to minimize downtime and disruption. Non-technical leaders do not need to understand model internals to insist that consistent vulnerability management coverage extends to every AI asset in the environment.
Regulatory Compliance and AI Governance Mapping
AI risk management software accelerates regulatory compliance by mapping controls and evidence to frameworks and laws. AI-based tools automate compliance monitoring and reporting tasks that would otherwise consume hours of manual effort each week. Documenting compliance alone is insufficient without continuous risk testing; these platforms combine documentation with active verification.
The EU AI Act was passed on May 21, 2024, and classifies AI systems based on risk levels, imposing obligations for high-risk systems around data governance, transparency, and human oversight. U.S. SMBs may not be directly regulated by the EU AI Act today, but partners and auditors increasingly expect demonstrated AI governance maturity. ISO 42001 is a standard for AI compliance that provides a management system framework similar to ISO 27001’s role in information security.
Platforms like Credo AI and others provide policy libraries, assessment templates, and automated evidence collection. NIST AI RMF provides guidance for AI risk management through its 2023 release (AI RMF 1.0) and its 2024 Generative AI Profile, which addresses risks specific to foundation models. These serve as credible reference points for developing risk mitigation strategies without the legal complexity of full regulatory interpretation.
TAG interprets these frameworks, customizes the control set for each client’s industry and risk profile, and implements them inside chosen risk management software for ongoing continuous monitoring. This is part of TAG’s broader IT consulting and risk assessment practice.
Shadow AI Visibility: Why You Need Risk Management Software
Shadow AI is the unauthorized or ungoverned use of AI tools, features, or accounts that IT and leadership cannot fully see or control. A 2026 report on shadow AI in SMEs found that 80% of employees bring unsanctioned AI tools to work, and companies with 11 to 50 employees average about 269 shadow AI tools per 1,000 employees. Nearly 40% of AI interactions in those businesses involve sensitive data.
AI risk management software helps detect shadow AI through several mechanisms:
- Monitoring unusual outbound traffic to AI APIs and services
- Flagging new SaaS tools with hidden AI features that were not part of the original approval
- Identifying unregistered model use in workflows
- Logging prompt interactions across governed platforms
The visibility questions these tools answer are concrete: What AI tools exist in our environment? What data do they access? Who owns each account? Is usage logged and auditable? If an employee left tomorrow, would their AI conversation history and company knowledge leave with them?
TAG’s position is straightforward: you cannot govern what you cannot see. Software plus process is how SMBs move from guesses to measurable responsible AI governance. For employees who need to experiment with AI safely, TAG’s AI Sandbox Services provide a governed alternative that reduces the pull of shadow AI without restricting productivity.

Comparing Approved AI vs Shadow AI
The table below helps executives see the concrete differences between governed AI usage and uncontrolled shadow AI activity. Each row represents a governance dimension where the gap between approved and shadow AI creates measurable risk.
| Dimension | Approved / Governed AI | Shadow AI |
|---|---|---|
| Ownership | Known; assigned to a team or department | Unknown or tied to an individual employee |
| Account administration | Managed by IT; centrally provisioned | Employee-created; personal or free-tier accounts |
| Data rules | Defined policies for what data can enter the system | No restrictions; any data may be pasted or uploaded |
| Visibility | Usage logged and reportable | Invisible to IT and leadership |
| Access control | Role-based; integrated with identity management | Open to anyone with the account credentials |
| Logging | Prompt history, API calls, and data access recorded | No organizational logs exist |
| Employee departure | Account revoked; data retained by organization | History leaves with the employee |
| Integrations | Reviewed and approved connections to other systems | Unknown connections; potential data leakage paths |
| Review process | Scheduled audits and risk assessments | No review; no accountability |
Shadow AI undermines risk management, data integrity, and regulatory compliance at every row. Only 13% of GRC professionals report full confidence that they know every AI tool in use across their organization, according to Drata’s 2026 State of GRC research. Shadow AI breaches cost an average of $4.63 million, $670,000 more than standard incidents.
AI risk management software, when properly configured by a partner like TAG, strengthens the “Approved AI” column across every dimension.
How AI Risk Management Software Supports a NIST AI RMF–Aligned Program
The NIST AI Risk Management Framework organizes AI risk practices into four core functions: Govern, Map, Measure, and Manage. The management framework AI RMF released in January 2023 provides a voluntary but widely referenced structure for responsible AI governance, and NIST’s 2024 Generative AI Profile extends this guidance to address risks specific to foundation models and generative AI.
Software aligns to each function:
- Govern: policy libraries, role assignments, ownership records, and approval workflows for each AI system. Leadership defines acceptable use; the platform enforces it.
- Map: AI asset inventories, data lineage tracking, and risk factor documentation. This is where organizations identify potential risks and catalog every AI tool, model, and integration.
- Measure: analytics, bias testing, drift detection, and performance monitoring. The platform produces risk ratings and evidence that controls are working.
- Manage: remediation workflows, human in the loop override capabilities, incident response integration, and regulatory control mapping. This function covers developing risk mitigation strategies and executing them.
For SMBs, the advantage is clear: instead of maintaining spreadsheets and ad hoc documents that quickly become outdated, they rely on a platform that embeds these framework concepts into daily operations. TAG handles the framework interpretation and implementation as part of broader risk assessment engagements, translating the AI RMF into a practical, right-sized program.
Choosing AI Risk Management Software: Criteria for SMBs
Selecting the right platform in 2026 requires matching tool capabilities to the realities of a 25 to 100 person business. Not every feature marketed to enterprises applies, and overspending on complexity creates its own risk: adoption failure.
Evaluation criteria that matter for SMBs:
- Ease of use and deployment: minimal setup, intuitive dashboards, low learning curve for non-technical staff.
- Integration with existing systems: can the tool connect to your identity directory, SIEM, cloud accounts, and ticketing system? Isolated tools create duplicate work.
- Coverage of the AI lifecycle: does the platform handle inventory, evaluation, policy enforcement, drift detection, and reporting, or only a subset?
- Framework support: look for visible alignment with the NIST AI RMF, ISO 42001, and regulatory libraries for HIPAA, GDPR, or Virginia privacy laws.
- Reporting capabilities: can the tool produce audit-ready evidence packages that satisfy your industry’s regulators or your clients’ expectations?
- Pricing scalability: does the pricing model make sense for a small user count? Avoid per-model or per-asset pricing that escalates unpredictably.
- Vendor support and transparency: what SLAs, customer support, and compliance guidance does the vendor offer?
Include both IT and business leadership in the selection process. The tool needs to align with actual workflows and compliance obligations, not just technical specifications. TAG serves as a neutral advisor in this process, helping compare options based on what fits the client’s environment rather than pushing a single vendor.
Integrating AI Risk Management Software with Existing IT and Security Tools
Standalone risk management tools lose effectiveness when disconnected from core systems. The value multiplies when AI risk data flows into the same environment where identity management, ticketing, SIEM, and disaster recovery platforms already operate.
Typical integrations include:
- Pulling security alerts into the risk platform for correlation with AI-specific events
- Pushing remediation tasks into service desk systems with assigned owners and deadlines
- Syncing user identities from directory services to enforce role-based access on AI tools
- Connecting to cloud provider logs to track AI API usage and data movement
In a TAG-managed environment, network monitoring, endpoint protection, and risk management software share information through a common data layer. When an endpoint detection tool flags unusual outbound connections to an AI service, the risk platform correlates that with user identity and data classification to determine whether it represents a shadow AI incident or approved usage. The response workflow triggers automatically in the ticketing system.
This integration reduces duplicate data entry and ensures AI-related issues are addressed within existing change and incident workflows. TAG’s managed IT and vendor management services simplify coordination among multiple software providers so the SMB’s internal team is not managing a dozen vendor relationships.
Implementing AI Risk Management Software: A Step-by-Step Roadmap
Adopting AI risk management software does not require a company-wide transformation on day one. A phased, low-disruption approach works best for SMBs.
The first phase is an initial risk assessment. Before selecting any tool, identify what AI exists in the organization, what data it accesses, and where the highest-priority gaps are. This baseline shapes every decision that follows.
The second phase involves requirements definition. Based on the assessment, define what the software must do. Does your industry require HIPAA mapping? Do you need shadow AI detection? Is generative AI usage a primary concern? These answers narrow the field.
Third, tool selection. Evaluate two or three platforms against the criteria outlined above, with input from both IT leadership and business stakeholders.
Fourth, pilot implementation. Start with one or two critical AI use cases or a single business unit. A healthcare practice might pilot with its patient-facing chatbot; a law firm might start with its document summarization workflow.
Fifth, policy configuration and training. Load acceptable use policies, configure alerting thresholds, and provide short, role-specific training so staff understand what the new governance means for their daily work.
Sixth, ongoing review. Set a calendar for quarterly AI risk reviews. Governance is not a project with an end date. It is a repeating function, similar to financial controls. Executive sponsorship and clear ownership for AI governance are critical, even in companies where people wear multiple hats.
TAG commonly leads these projects end-to-end, aligning technical implementation with broader cybersecurity and business continuity plans.

Common Pitfalls and How to Avoid Them
Many AI risk management efforts fail not because of technology, but because of unrealistic scope, poor communication, or lack of follow-through.
Treating software as a silver bullet. A tool without process change produces dashboards that nobody acts on. Countermeasure: define a small, well-scoped policy set before deploying any platform, and assign named owners for every action item.
Ignoring shadow AI. About 77% of small businesses using AI have no written AI policy, according to the 2026 shadow AI in SMEs report. Pretending the problem does not exist guarantees blind spots. Countermeasure: run a blameless survey asking employees what AI tools they use, then build the inventory from honest answers.
Overcomplicating controls. Applying the same strict governance to a low-risk internal summarization tool as to a system processing PHI wastes resources and frustrates staff. Countermeasure: tier controls by actual risk level. Not every AI use case needs the same review depth.
Failing to train staff. Policies that exist only in a shared drive and are never discussed become irrelevant within weeks. Countermeasure: keep training short, role-specific, and recurring.
Not assigning a clear owner. AI governance without accountability drifts. Countermeasure: designate someone, whether internal or through a managed partner like TAG, to review AI usage and policy on a set schedule.
TAG’s role includes coaching leadership teams through these adoption challenges. AI risk management is an ongoing practice, not a one-time IT project.
How TAG’s AI Sandbox and Cybersecurity Services Complement AI Risk Tools
An AI sandbox is a governed environment where employees can experiment with AI tools under centralized monitoring, clear data rules, and defined boundaries. Instead of choosing between banning AI entirely and allowing uncontrolled adoption, an AI sandbox provides a practical middle path for secure AI adoption.
TAG’s AI Sandbox Services integrate with AI risk management software by feeding usage logs, policy enforcement results, and risk metrics into a central console. Employees get access to approved tools. Leadership gets visibility. Data stays within governed boundaries.
This connects to TAG’s broader cybersecurity and risk assessment services for a full-picture approach: IT support, security, and AI governance working together under one managed relationship. The combination helps SMBs make safe, governed AI easier to use than shadow AI.
Your team does not need less access to AI. You need better visibility into how they are using it. Contact TAG to discuss how to identify and govern shadow AI in your organization without slowing employees down.
FAQ: AI Risk Management Software and Frameworks
These concise, answer-first responses address common executive questions about AI risk management software and related governance topics.
What is AI risk management software? AI risk management software is a platform that helps organizations identify, assess, monitor, and mitigate risks specific to artificial intelligence systems, including model behavior, data access, bias, and regulatory compliance. It differs from generic security tools by focusing on the AI lifecycle: inventorying models, tracking data lineage, monitoring drift, and enforcing acceptable use policies.
How is it different from traditional risk management software? Traditional risk management software focuses on IT risks like malware, access control, and network vulnerabilities. AI risk management software extends that focus to cover AI-specific issues: prompt logging, model versioning, training data governance, bias detection, and shadow AI discovery.
Do small businesses really need AI-specific tools? Yes. 95% of U.S. companies utilized AI in production by 2023, and most SMBs already use multiple AI-powered features across their SaaS stack. Without risk-specific visibility, they face exposure to data breaches, regulatory non-compliance, and financial risks.
What is the NIST AI RMF? The NIST AI Risk Management Framework (AI RMF 1.0), released in January 2023, is a voluntary U.S. framework that organizes AI risk practices into four functions: Govern, Map, Measure, and Manage. NIST released a Generative AI Profile in 2024 with additional guidance for foundation models.
How do these tools help with regulatory compliance? They map organizational controls and evidence to frameworks and laws, including the EU AI Act, NIST AI RMF, ISO 42001, HIPAA, and state privacy regulations. Automated evidence collection and reporting reduce the manual burden of audit preparation.
Can AI risk management software detect shadow AI? Yes. These tools monitor for unusual API traffic, new SaaS integrations with AI features, unregistered model usage, and data flows to unapproved AI services. They help answer the basic governance questions: what exists, what data it touches, and who owns it.
How often should we review AI risks? Quarterly at minimum, with continuous monitoring between reviews. Regular risk assessments keep governance current as vendors add new AI features and employees adopt new tools.
Who should own AI governance in a 25 to 100 person company? Someone must be accountable, whether that is an internal IT leader, a COO, or a managed services partner acting as virtual CIO/CISO. TAG fills this role for many SMBs, overseeing AI governance and tool selection under a flat-rate IT model.
What is an AI sandbox? An AI sandbox is a governed environment where employees can use approved AI tools with centralized monitoring, defined data rules, and usage logging. It provides a safe space for AI adoption that reduces shadow AI without restricting productivity.
Conclusion: Turning AI Risk into a Managed, Measurable Practice
AI risk management software, combined with a clear risk management framework and expert guidance, turns AI from a vague concern into a measurable, governable part of the business. The tools exist. The frameworks exist. The gap for most SMBs is implementation and ownership.
Visibility comes first. You cannot govern what you cannot see, and AI risk management software is how you build that visibility. Whether the concern is shadow AI, regulatory compliance, data integrity, or ethical AI practices, the starting point is the same: know what AI exists, know what data it touches, and assign someone to review it.
Do not wait for a regulation or an incident to force the conversation. Start with an AI risk assessment, implement a small set of high-impact controls, and build from there. An AI strategy does not need to be complex to be effective. It needs to be owned, measured, and reviewed.
Richmond-area business leaders can contact Technology Assurance Group to discuss AI governance, secure AI adoption, and integration with existing managed IT and cybersecurity services. TAG is here as a long-term strategic technology advisor, helping you treat AI risk as a business function, not a project.